Summary:
What does New York PHL §2832 mean for hospital visitor management.A healthcare visitor management system (VMS) is software that manages a hospital visitor’s entire visit—identity verification, patient and appointment validation through the EHR, policy screening, badge issuance, access-control permissions, location awareness, security exception alerts, and checkout. New York Public Health Law §2832 requires general hospitals to assess visitor management and access control as part of an annual workplace safety and security assessment. It does not mandate any specific product, but it makes “check in and print a badge” a hard thing to defend as a complete visitor-management program. Athena Security’s healthcare VMS, Entrance Pass, is a purpose-built hospital visitor management system available on the Apple App Store and listed on the Epic Showroom. |
What is New York PHL §2832?
New York Public Health Law §2832 is a hospital workplace violence prevention statute. It was enacted as A.203-B (Cruz)/ S.5294-B (Sepulveda) and signed by Governor Hochul as Chapter 618 of the Laws of 2025. The law requires general hospitals and nursing homes to establish a workplace violence prevention program and, for general hospitals, to conduct an annual safety and security assessment that considers the facility’s layout and access points, visitor management, access control, engineering controls, alarms and communication systems, staffing, training and security procedures. The stated purpose is protecting healthcare workers, patients, families and visitors.
Key dates for hospital leaders (confirm against the chaptered text and any Department of Health guidance):
| Date | Milestone |
|---|---|
| January 1, 2027 | Annual workplace safety and security assessment and written plan required for general hospitals |
| September 18, 2026 | Section effective |
| December 12, 2025 | Signed as Chapter 618 of the Laws of 2025 |
The law also requires a workplace violence incident log, information for employees on how to report incidents, and sharing of redacted incident summaries and trend data with the hospital’s security or safety committee.
Does PHL §2832 require a specific visitor management system?
No. PHL §2832 does not mandate Athena Security, AI cameras, barcode tracking or automatic checkout. It requires each general hospital to assess its own risks and adopt measures appropriate to the threats it identifies. Visitor management and access control are expressly named as factors the assessment must consider.
That creates the practical question every New York hospital security director will face in the assessment:
Does our visitor management system actually manage the visitor—or does it stop when the badge comes out of the printer?
Why are most hospital visitor management systems incomplete?
Most visitor management software is built around the front desk. A visitor arrives, an ID is scanned, a screening check may run, and a badge prints. That answers one question: who is this person at check-in?
Hospital security has a longer list of questions after the badge is printed:
- Is the visit authorized against an actual patient, room or appointment?
- Is the visitor still authorized right now, or has the badge expired?
- Should this credential open this elevator, turnstile or door?
- Where was the visitor’s badge last recorded?
- Is the person on a BOLO list, restricted-person list or internal watchlist?
- If there’s an incident, can an officer see who they are, why they’re here and their prior visits?
- Did the visitor actually leave?
A healthcare-specific VMS has to answer those questions, not just the first one.
What should a healthcare visitor management system do?
A complete hospital visitor lifecycle looks like this:
flowchart TD
    A[Identify visitor] --> B[Validate patient / appointment via HL7 ADT]
    B --> C[Apply hospital visitor rules + BOLO / screening]
    C --> D[Issue unique badge with permissions]
    D --> E[Badge activates authorized elevator, turnstile, door]
    E --> F[Record barcode + access events]
    F --> G{Exception?}
    G -- Yes --> H[Image-backed alert to security; deny access]
    G -- No --> I[AI exit workflow detects exit]
    H --> I
    I --> J[Automatic checkout]
    J --> K[Reporting + visit history]
Every step after the badge prints is where a basic VMS stops and a healthcare VMS keeps working.
Athena’s approach with Athena Healthcare Visitor Management (Entrance Pass) is to automate the routine parts of that lifecycle so trained security personnel spend their time on the exceptions that require human judgment.
Does Athena Healthcare Visitor Management integrate with Epic and Oracle Health/Cerner?
Yes. Athena Healthcare Visitor Management integrates with Epic, Oracle Health/Cerner and other healthcare systems that can supply a compatible HL7/ADT feed. Entrance Pass is listed on the Epic Showroom. Depending on the hospital’s interface configuration, the visitor workflow can use patient identity, patient status, room, floor, department, appointment information, confidentiality flags and other configured visit-validation fields.
The integration is purpose-limited: the VMS uses the fields needed to validate a visit, not the patient’s medical record, and operates under the hospital’s privacy, security, access and retention policies.
Why HL7/ADT integration matters at the front desk
A visitor says, “I’m here to see John Smith in Room 517.” Without EHR integration, staff take the visitor’s word, call the unit, or search a second system. With a compatible HL7/ADT feed, the workflow becomes:
Identify visitor → Validate the visit against hospital-provided patient data → Apply visitor rules → Issue credential
Because it works through HL7/ADT rather than a single vendor API, the same workflow supports Epic, Oracle Health/Cerner and other compatible environments.
Can a hospital visitor badge control elevators, turnstiles and doors?
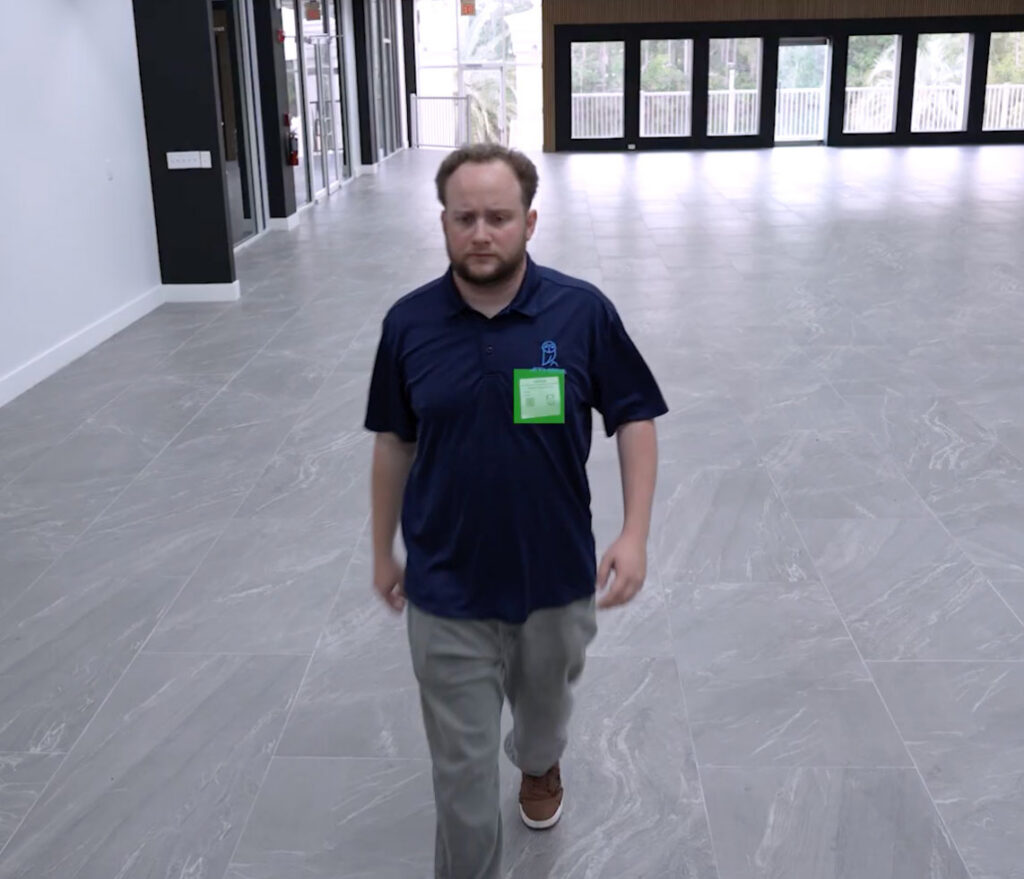
Yes, when the Athena Heathcare VMS is integrated with the hospital’s access-control system. A printed badge is passive—”Floor 5″ or “Expires 3:00 PM” only works if someone notices the visitor on Floor 7 at 3:30.
With Athena, the visitor badge carries configured permissions tied to the visit. A visitor authorized for a patient on the fifth floor receives credentials for the fifth-floor elevator and the doors along that route. If the badge is valid for the access point, access is permitted under the hospital’s rules. If it’s expired or not authorized for that location, access can be denied where the integration is deployed.
The badge stops describing what the visitor may do and starts enforcing it.
Video: Watch Athena Healthcare VMS Elevator & Turnstile Access Control
Caption: Athena Healthcare Visitor Management connects a visitor badge to configured access control so an authorized credential activates approved elevators, turnstiles and doors.
What happens when a visitor badge expires or the visitor is in the wrong place?
This is where visitor management moves from passive identification to active exception management.
When a configured rule triggers—an expired badge, a credential presented at an unauthorized location, a BOLO match—Athena can generate a security alert with an image associated with the person and the event. Depending on configuration, the alert can include:
- Visitor name and identifying information
- Event image
- Visitor type and reason for the current visit
- Patient or department context (where appropriate)
- Badge status and expiration
- Location or access point where the alert occurred
- Last known badge location
- Previous visit history and prior security events
- BOLO, restricted-person or watchlist status
- Approved third-party screening results (sex-offender or child-safety screening) where those services are used
If access control is integrated at that point, the system can also deny the request. Instead of an officer seeing only ACCESS DENIED, the officer sees who the person is, why they’re here, where they’re supposed to be, why access was denied, when they last visited, and where their credential was last recorded—before or while responding.
Can Athena show a visitor’s previous visits?
Yes, subject to the hospital’s configuration, user permissions and retention policy. Authorized security users can see when a person last visited, their current purpose, destination, badge status, last known badge location, prior configured security events and applicable flags. Hospital-maintained BOLO lists, restricted-person lists and internal watchlists become part of the workflow, and approved third-party screening results can surface alongside them.
A visitor alert doesn’t exist in isolation; it arrives with the visitor’s history.
How does Athena provide visitor location awareness without facial recognition?
Athena prints a unique barcode on each visitor badge. Hospitals place barcode scanners at configured points—entrances, elevator banks, department entries, exits. Each scan records an event and updates the visitor’s last known badge location:
Main entrance → Elevator bank → Patient tower → Department → Exit
This is credential-based location awareness, not continuous person tracking. Athena does not claim GPS-style knowledge of where someone is every second, and this approach does not require continuously identifying people through facial recognition.
Why is visitor checkout such a problem in hospitals?
Traditional visitor management depends on the visitor to check out—return to the desk or scan a badge on the way out. In a hospital, people leaving are focused on a family member, a child, a diagnosis or their car. When they forget, the system keeps showing them as active.
That creates a gap between two questions:
- Who checked into the hospital today?
- Who is still listed as an active visitor right now?
For an incident, an evacuation or a security report, only the second question is useful.
How does AI-powered automatic visitor checkout work?
Athena’s configured AI-assisted exit workflow identifies when a visitor has left and closes the visitor session automatically. The dependency chain changes from:
Visitor walks out → Remembers scanner → Scans badge → Visit closes
to:
Visitor exits → AI exit workflow identifies the event → Visit closes automatically
The goal is a more accurate active-visitor list without stationing an employee at every exit to remind people to check out. This is not a claim of perfect continuous tracking—it is a way to reduce reliance on voluntary checkout behavior.
Why not just staff every exit and elevator?
A hospital can. But large campuses have dozens of entrances, exits, floors and routes, and PHL §2832 itself contemplates a mix of measures—staffing, engineering controls, alarms, communications, safety equipment, facility modifications and other appropriate measures—based on each hospital’s assessment. Technology and personnel aren’t substitutes. Automation handles the repetitive work; officers handle suspicious behavior, de-escalation, incident response and investigations.
How does hospital visitor reporting support §2832 documentation?
The annual assessment and incident log requirements reward hospitals that can produce a real visitor record. Athena reporting gives authorized users the visitor lifecycle: who checked in, visitor type, visit reason, patient or department context, check-in time, current status, badge expiration, barcode location events, last known badge location, previous visits, checkout information and configured security exceptions.
Instead of John Smith — Checked in 10:14 AM, security has the status and history of the visit.
Video: Watch Athena Healthcare VMS Visitor Reporting & Awareness
Caption: Athena Healthcare Visitor Management reporting gives hospital security teams visibility into visitor status, visit history and location events across the visitor journey.
How do integration, access control, alerts and checkout work together?
One end-to-end visit:
- Visitor arrives; Athena identifies the visitor
- Visit is validated using Epic, Oracle Health/Cerner or another HL7/ADT source
- Hospital visitor and security rules are applied, including BOLO and screening checks
- Badge prints with visit-specific permissions
- Badge activates the authorized elevator, turnstile or door
- Barcode and access events record visitor location context
- An expired or unauthorized credential generates an image-backed alert
- Integrated access control denies the unauthorized request
- AI-assisted exit workflow detects the visitor leaving
- Visit closes automatically
- Reporting preserves the visit history
That is a healthcare visitor management system. Scan ID → Print badge → Visitor disappears into the hospital is a lobby registration system.
How does visitor management fit with weapons detection?
They answer different questions in a layered hospital entrance:
| Layer | Question it answers |
|---|---|
| Visitor management | Who is this person, why are they here, are they authorized, where can they go, is the credential still valid, have they left? |
| Weapons detection | Is someone entering with a weapon or prohibited item? |
| X-ray screening | What is inside the bag? |
| Access control | Should this credential open this point? |
| HL7/ADT integration | What patient and appointment context applies? |
No single layer eliminates every risk. A §2832 assessment that considers layout, access points, visitor management and access control together is, in effect, an assessment of how well those layers work as one system.
What should New York hospitals evaluate before January 1, 2027?
Map the complete visitor journey from entrance to exit and ask:
- How is visitor identity established?
- How are patients and appointments validated—and can the VMS talk to Epic, Oracle Health/Cerner or another HL7/ADT source?
- What does the badge actually authorize, and can it control elevators and turnstiles?
- What happens when a badge expires?
- How is an unauthorized-location event detected?
- Does security receive an image with visitor context, and can access be denied automatically?
- Can security see prior visits, BOLO status and last known badge location?
- How does the hospital know a visitor has left, and does checkout depend on people remembering to do it?
And the question that cuts through all of it:
If a security incident happened right now, what could our visitor management system actually tell the security team?
About Athena’s product philosophy
Athena’s healthcare VMS follows the same design principle as the rest of its portfolio: sophisticated security technology should be simple to operate, highly automated and built for the environment it protects. In September 2026, Fast Company awarded Athena Security’s Ambulance Bay Weapons Detection System an innovation by design in the Established Excellence category of its 2026 Innovation by Design Awards.
That recognition was for the weapons detection system, not the VMS—but the philosophy is the same: eliminate repetitive manual work, connect to hospital systems, make the badge enforce permissions, let software find the exceptions, and give officers enough context to act.
Frequently asked questions
What is a healthcare visitor management system?
Software that manages a hospital visitor’s full lifecycle: identity verification, EHR-based visit validation, policy screening, badge issuance, access-control permissions, location awareness, exception alerts, checkout and reporting.
Does New York PHL §2832 require a visitor management system?
No. It requires general hospitals to conduct an annual workplace safety and security assessment that considers visitor management and access control, and to adopt measures appropriate to identified risks.
When do New York hospitals have to comply with PHL §2832?
The section is effective September 18, 2026, with the annual assessment and plan requirement for general hospitals beginning January 1, 2027. Hospitals should confirm dates against the chaptered law and Department of Health guidance.
Can a visitor management system integrate with Epic?
Yes. Athena Healthcare Visitor Management (Entrance Pass) integrates with Epic, Oracle Health/Cerner and other systems through HL7/ADT feeds to validate patient, room, department and appointment context at check-in. It is listed on the Epic Showroom.
Can a hospital visitor badge open elevators and doors?
Yes, when the VMS is integrated with the hospital’s access-control system. Permissions are tied to the specific visit and can be denied when the badge expires or is used at an unauthorized location.
What is automatic visitor checkout?
An AI-assisted exit workflow that detects when a visitor leaves and closes the visit automatically, so the active-visitor list doesn’t depend on visitors remembering to scan out.
Does Athena use facial recognition for visitor tracking?
Visitor location awareness is based on barcode badge scans at configured points—credential-based location events, not continuous facial-recognition tracking.
Where can hospitals get Entrance Pass?
Entrance Pass is available on the Apple App Store and listed on the Epic Showroom.
Healthcare visitor management should manage the visit from entrance to exit—not just print the badge. For New York general hospitals, that is now a question the annual §2832 assessment will ask directly.
Sources
-
New York State Senate — Public Health Law §2832, Violence Prevention Program
- New York State Assembly – A203 bill text (PHL §2832)
- New York State Senate – S5294B
- New York State Senate – A203B
- Governor Hochul signs hospital violence prevention bill, Chapter 618 of the Laws of 2025
- Fast Company 2026 Innovation by Design Awards
- Entrance Pass – Apple App Store
- Entrance Pass Visitor Management by Athena – Epic Showroom